Insights / Governance & Risk
Unlocking Cyber Resilience: A Closer Look at NIST Cybersecurity Framework 2.0
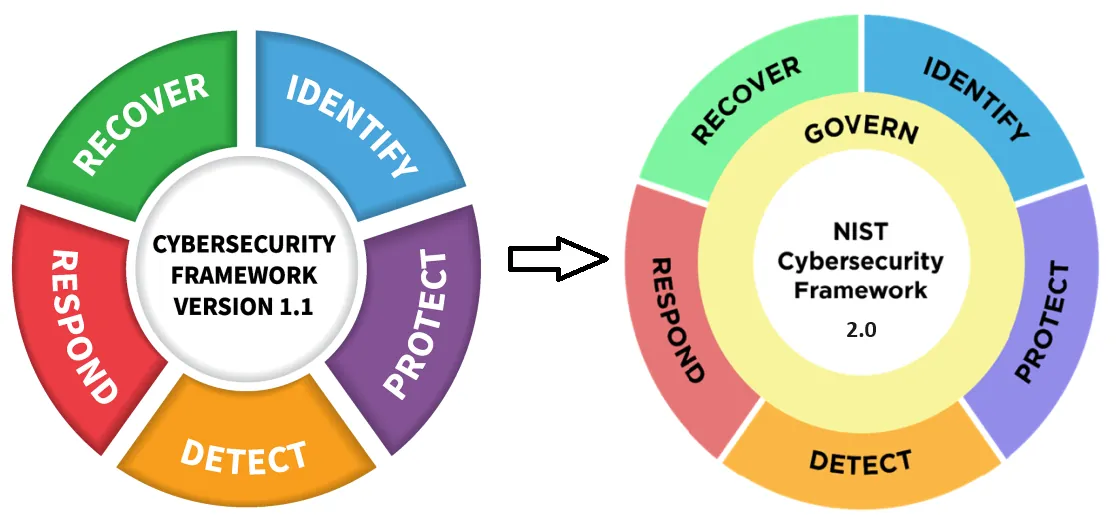
In the face of escalating cyber threats, the need for robust defenses has become paramount. Recognizing this urgency, the National Institute of Standards and Technology (NIST) has unveiled Cybersecurity Framework Version 2.0, a landmark advancement in organizational cyber resilience.
Governance Takes Center Stage
This iteration introduces a groundbreaking "Govern" function, emphasizing the crucial role of executive leadership and strategic decision-making in cybersecurity. Gone are the days of siloed cybersecurity efforts. Version 2.0 champions its seamless integration into enterprise risk management, fostering clear roles, responsibilities, and active executive engagement.
Strengthened Core Functions
The framework undergoes a comprehensive overhaul, enhancing core functions like Identify, Protect, Detect, Respond, and Recover. The revamped framework emphasizes understanding the business context to prioritize assets effectively. The expanded Asset Management category now encompasses dynamic elements like data flows and external dependencies, reflecting the ever-evolving cyber landscape. Additionally, dedicated focus on Governance and Risk Assessment equips organizations to navigate both internal and external threats with confidence.
Addressing the Interconnected Landscape
Acknowledging the interconnectedness of modern business ecosystems, Version 2.0 introduces robust Supply Chain Risk Management (SCRM) guidelines. These guidelines establish cybersecurity requirements for suppliers, map information flows, and strategize responses to potential disruptions, building resilience across the entire ecosystem.
Measurability and Adaptability
Version 2.0 prioritizes outcome-focused measurability, aligning with established standards like NIST SP 800-55. The refined concept of "Tiers" empowers organizations to effectively gauge their governance, risk management processes, and awareness of third-party risks.
Seamless Integration and Enhanced Compatibility
Beyond these core changes, Version 2.0 comes equipped with practical implementation guidance and customizable templates, facilitating smooth integration into existing organizational frameworks. Furthermore, its improved compatibility with other widely used cybersecurity frameworks like ISO 27001 and COBIT enhances its utility across diverse organizational contexts.
A Beacon of Guidance in an Evolving Landscape
NIST Cybersecurity Framework Version 2.0 represents a monumental leap in the ongoing pursuit of cyber resilience. By embracing the principles of governance, risk management, and outcome-focused measurability, organizations can build robust defenses against the ever-evolving threat landscape. As the digital frontier continues to face new challenges, Version 2.0 stands as a beacon of guidance empowering organizations to navigate the complexities of cybersecurity with confidence and resilience.
Originally published on LinkedIn · February 26, 2024